

Your security team receives a file-change alert from a Sitecore-connected production environment. A configuration file has a new hash, the timestamp falls outside the normal deployment window, and the affected host also runs connectors used by content publishing and search. The alert tells you what changed, but not whether an administrator applied an emergency fix, a pipeline deployed an approved release, an automated platform task introduced drift, or an attacker modified the system.
That distinction defines the core value of file integrity monitoring, or FIM. In modern digital experience platforms, FIM isn't a weekly compliance snapshot applied to a static server. It must connect file changes with deployment provenance, identity, application activity, cloud events, and incident response. Sitecore XM Cloud, Sitecore Stream, AEM, and SharePoint estates all create different monitoring boundaries, especially when presentation, content, infrastructure, and AI-assisted workflows are distributed across managed services.
Table of Contents
- Monitoring agents and scoped coverage
- Centralized logging and correlation
- Tamper resistance and response
Understanding File Integrity Monitoring
A security analyst sees a modified system file and opens an investigation. The first question is simple: what changed? The file's hash differs from its trusted baseline, its ownership may have changed, or the system may report a new file in a sensitive directory. FIM can surface that deviation, but the analyst still needs a second answer: was the change legitimate?
An approved operating-system update, a Sitecore deployment, an emergency administrator fix, and a malicious persistence mechanism can all produce file events. Treating every deviation as a compromise creates noise. Treating every expected deployment as harmless creates a blind spot. FIM works when the security team can compare the event with a release record, the responsible identity, the process that made the change, the timestamp, and the originating host.
The original Tripwire model demonstrates why FIM began as a forensic and intrusion-detection control, not just a change-management feature. At Purdue University, Gene Kim and Eugene Spafford developed Tripwire in 1992 for Unix systems. It created cryptographic signatures, recorded file attributes, and compared those trusted baselines with later observations. Tripwire was released publicly on November 2, 1992, to more than 100 beta-testing sites worldwide, followed by four updates in 1993 and its first formal release in December 1993. The historical Tripwire artifact documents the operating model that remains familiar today.
Detection is only half the control
A changed hash is a signal, not a verdict. The signal becomes useful when the surrounding evidence lets a team classify it as approved maintenance, accidental drift, malware activity, or insider action.
That classification matters even more on a digital experience platform. Frequent releases, content operations, integrations, personalization rules, and scheduled maintenance can modify related assets through different paths. A FIM policy that can't distinguish those paths will either overwhelm engineers or miss the modifications that affect trust, availability, and regulated data.
How File Integrity Monitoring Works
Every FIM implementation follows the same basic cycle, even when the platform uses different agents, event collectors, or cloud audit APIs.
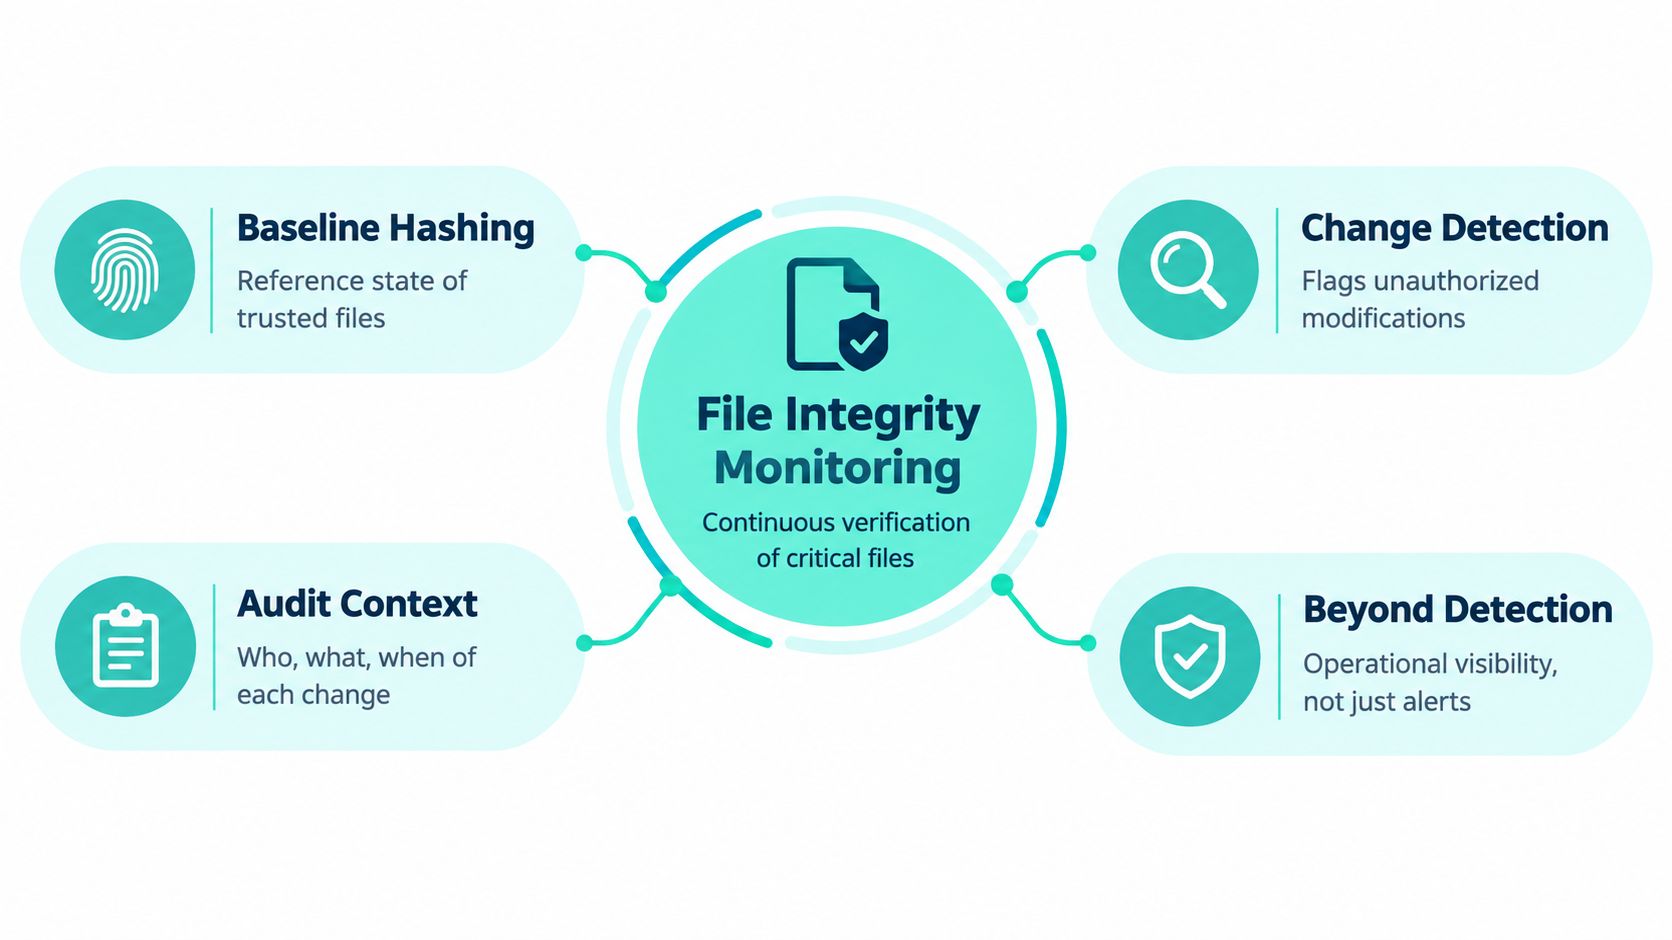
Establish a trusted baseline. Build the reference state from a verified production build, not from an unreviewed host that may already contain drift. Record cryptographic hashes and relevant metadata for security-sensitive files, directories, executables, libraries, configurations, audit logs, databases, and backups.
Select the monitoring scope. Define which paths and attributes matter. A system binary may require content, ownership, permissions, and timestamps. A log location may need different handling because its contents change as part of normal operation. A Sitecore deployment artifact, configuration manifest, or secrets-management integration deserves a policy that reflects its role rather than a blanket rule applied to every temporary file.
Scan or observe changes. FIM can perform scheduled comparisons, event-driven checks, or both. Early Tripwire documentation described regular checks of designated files and directories, including daily scans, with alerts for corrupted or altered content. The choice between periodic and near-real-time detection depends on risk, system behavior, and the response capability available to the team.
Compare current characteristics with the baseline. A practical enterprise baseline uses a cryptographic fingerprint and metadata. SHA-256 is a practical minimum for content fingerprints because it is specified by FIPS 180-4. A replacement binary, altered SSH key, or tampered audit log should produce a different digest.
Alert with context and respond. The alert should identify the path, change type, timestamp, identity, process, ownership, permissions, and host where available. Analysts then correlate it with deployment events, administrator activity, endpoint telemetry, and change-management records before accepting a new state or opening an incident.
A baseline must remain trustworthy after creation. Store it with restricted write access or seal it externally, then refresh it only through controlled change management. If the same administrator or compromised host can rewrite both the monitored file and the reference database without detection, the control loses much of its evidentiary value. For teams designing operational alerting around Azure workloads, Azure monitoring alerts and their surrounding practices provide useful implementation context, but FIM still needs its own scope and response logic.
Enterprise FIM Architecture and Components
A production FIM capability is a distributed evidence pipeline, not a scanner installed on a few servers. The architecture must collect changes close to the asset, centralize records away from the monitored host, enrich events with enterprise telemetry, and trigger a response that someone can execute.
Monitoring agents and scoped coverage
Agents or collectors observe files, directories, permissions, ownership, and other defined attributes on supported hosts. Their value depends on scope. Monitoring every transient build artifact and container layer may generate a large amount of low-value activity, while ignoring deployment manifests, web-server configuration, application binaries, and audit-log locations leaves meaningful gaps.
For Sitecore, AEM, and SharePoint-connected systems, coverage should reflect the platform's actual trust boundaries. A collector may monitor a host-level configuration directory, while a separate integration captures deployment events, identity changes, content operations, or managed-service audit records. The objective isn't to force every asset into a file hash. It's to preserve enough evidence to determine whether a security-relevant state changed.
Centralized logging and correlation
FIM events should leave the monitored host and enter a separate security monitoring plane. NIST's data-integrity reference architecture recommends combining file-integrity logs with Windows, Linux, application, and database sources. That correlation turns a bare deviation into an investigation trail.
A useful event record answers several questions:
| Evidence | Operational question |
|---|---|
| File path and hash | What asset changed? |
| Timestamp | When did the change occur? |
| Identity and process | Who or what made it? |
| Deployment record | Was it part of an approved release? |
| Host and ownership | Where did it originate, and who controls the asset? |
| Preserved audit trail | Can the team reconstruct and defend the conclusion? |
Tamper resistance and response
Attackers who can alter a file may also try to erase the evidence. Centralized retention helps, but audit trails should also use digital signatures or integrity seals. NIST notes that signatures can alert on audit-trail alteration, although they don't prevent deletion. That limitation matters when designing retention, access controls, and incident procedures.
Response workflows close the gap between detection and action. A high-risk unauthorized production change should create an incident or trigger a controlled rollback. An approved deployment should be linked to its release record and closed without forcing an analyst to manually suppress each event. Ticketing, escalation rules, SIEM integration, and retention policies should be designed together, not added after the first alert flood.
The Cloud-Native FIM Challenge
Traditional FIM assumes a relatively stable server. A hash is created, the server remains in place, and later scans compare the current filesystem with the trusted state. Cloud-native digital experience platforms break that assumption through object storage, containers, ephemeral workloads, infrastructure-as-code, managed SaaS components, and automated redeployment.
The old question is, what changed on this server? The modern question is, which change is security-relevant in an environment designed to change continuously? A new container instance may be expected. A modified deployment manifest may be routine in a development branch but dangerous when it reaches production. A changed permission on object storage, pipeline definition, content connector, or infrastructure resource may matter more than a short-lived filesystem event.
The answer is a coverage model with explicit ownership boundaries:
- Host-owned assets: Monitor operating-system files, application binaries, web-server configuration, scheduled-task definitions, secrets-management integrations, and audit-log locations where direct file visibility exists.
- Pipeline-owned assets: Correlate build outputs, configuration-as-code, deployment manifests, release identities, and promotion events with production observations.
- Platform-owned services: Use provider audit events and service-specific controls when a managed component doesn't expose filesystem access.
- Content-owned changes: Distinguish approved content publishing, permission updates, templates, connectors, and automation from out-of-band modifications.
Broader monitoring isn't automatically better. Tracking every transient artifact increases noise and can hide the changes that affect trust, availability, or regulated data. A focused cloud-native architecture perspective is useful here, as is this discussion of the business value of cloud-native, because the operational benefits of distributed delivery also create more places where ownership and evidence must be defined.
A useful design doesn't pretend that a single FIM agent can see everything. It combines file observations with cloud audit events, CI/CD records, identity context, and configuration policy. That approach preserves the core integrity principle while adapting it to systems that are intentionally ephemeral.
FIM for Sitecore and Modern DXPs
Sitecore XM Cloud changes the implementation target immediately. Sitecore documents XM Cloud as a headless-only platform built with the JavaScript Rendering SDK, Sitecore Experience Edge, and a Jamstack framework or .NET Core client application. It doesn't support MVC-based solutions, so a security design can't rely on traditional server-file monitoring of a monolithic presentation layer. Sitecore's XM Cloud and Personalize documentation sets out that architectural constraint and distinguishes Sitecore Personalize from XP.
For XM Cloud, FIM should cover the parts the organization controls:
- Deployment artifacts and manifests, including the files and definitions promoted through CI/CD.
- Front-end application outputs, where a changed bundle or configuration can alter delivered behavior.
- Connector and integration settings, especially where identity, search, analytics, or external systems are involved.
- Secrets-management integrations, without exposing secret values in monitoring records.
- Audit and deployment evidence, linked to the release identity and environment.
Sitecore Stream expands the integrity conversation beyond generated text. Sitecore describes Stream as an AI layer spanning CMS, XM Cloud, Content Hub, CDP, Personalize, Search, and Connect. It includes brand kits, AI-enhanced workflows, generative copilots, visual search, natural-language answers based on content collections and Search domains, and Page Builder actions that can generate or refine component content. Page Builder can also support A/B/n testing of AI-generated variants against originals. The Sitecore Stream AI capabilities documentation provides the product detail.
AI artifacts need provenance
A FIM alert around an AI-enhanced workflow shouldn't be treated like a binary replacement. The relevant evidence may be a changed prompt configuration, brand-kit guidance, workflow permission, content variant, connector, or automation rule. Sitecore's 2025 product expansion describes distinct mechanisms including XM Cloud A/B/n testing, Search visual similarity and semantic search, reverse-image and color-based asset search, Stream copilots, and agentic workflows ranging from human-in-the-loop operation to fully agentic execution. The same release states that the Stream content copilot is available for XP 10.2 and later. Sitecore's 2025 product announcement should be read alongside deployment and identity records.
AEM requires the same principle, adapted to its repository, deployment, dispatcher, cloud configuration, and integration boundaries. SharePoint Online requires another adjustment because many controls are service-level and administrative rather than filesystem-level. For SharePoint solutions, monitor SPFx packages, provisioning definitions, Power Platform connections, privileged changes, audit events, and content or permission operations through the telemetry available to Microsoft 365. A Sitecore security patching guide can support the maintenance side, but patch validation and FIM are separate controls. One confirms authorized software maintenance. The other helps expose unexpected state changes.
Operational Best Practices for FIM
The strongest FIM programs begin with a narrow, defensible scope. Start with assets whose modification would affect security, delivery, auditability, or business continuity. On a Sitecore or AEM estate, that typically means deployment artifacts, application binaries, web-server configuration, secrets-management integrations, scheduled tasks, infrastructure definitions, and audit-log locations rather than every cache and temporary file.
Build a baseline you can defend
Create the baseline from a verified production build. Protect the reference with restricted write access or external sealing, and document who can approve a refresh. A legitimate release should produce a controlled baseline update after validation. An unexplained change shouldn't be accepted merely because the application still works.
Use the attributes that match the asset. Hashes detect content replacement. Ownership and permissions expose access-control drift. Timestamps help establish sequence. Process and identity context help explain cause. For a CMS deployment, these fields are more useful together than as isolated alerts.
Triage by provenance and impact
A practical triage model ranks events by both business impact and provenance:
- Approved pipeline and expected artifact: Link the event to the release, confirm the artifact, and close it through the normal change record.
- Privileged manual change: Validate the emergency or administrative record, confirm the operator, and review the resulting state.
- Service-account change outside a deployment window: Escalate for identity and process investigation, especially when the account normally performs automated work.
- Security-sensitive configuration change with no provenance: Treat it as a potential incident until the team establishes a trusted explanation.
Teams should track mean time to validate, false-positive rate, exception age, and the share of alerts connected to a ticket or incident. Alert volume alone rewards suppression, not reliable investigation. For additional guidance on reducing false positives in security alerts, the operational lesson is straightforward: improve scope and context before lowering sensitivity.
Integrate, don't forward blindly
Route FIM events into the SIEM with deployment, EDR, identity, application, and cloud audit evidence. Preserve the original event and its timestamps, then add the investigation outcome. High-risk systems may need near-real-time detection, while lower-risk assets can use scheduled comparisons aligned with their threat and audit requirements.
A website security best-practices guide can complement the platform view, but it shouldn't replace a FIM-specific operating model. Define who investigates, who can approve a baseline change, who can authorize rollback, and how the team handles a change that is both urgent and unexplained.
Building a Mature FIM Program
Maturity begins when FIM becomes part of platform operations rather than a report generated for an audit. Security, Sitecore, AEM, SharePoint, cloud, identity, and release teams need a shared view of trusted state. Each group owns different evidence, and the program must connect those records without pretending that one tool provides complete visibility.
Tune the control around business risk
A mature policy is selective. It watches assets that influence authentication, deployment, application execution, configuration, auditability, and regulated information. It excludes or treats volatile locations differently when their normal activity would bury high-value events. The team reviews those exclusions as the architecture changes.
This is particularly important for AI-enhanced Sitecore environments. A changed brand kit, workflow permission, search configuration, content variant, or personalization rule may not appear as a conventional server-file modification. The program therefore combines FIM with product audit events, release records, identity telemetry, and approval history. Sitecore XM Cloud Plus extends AI-supported capabilities across search, personalization, customer data, analytics, and Content Hub One, including on-brand text and image generation, intent-aware search, and visual asset discovery. Sitecore's XM Cloud Plus announcement illustrates why integrity governance must cover more than generated copy.
Make every alert lead somewhere
A useful program has a defined outcome for each event:
- Validated change: The team records the release, identity, scope, and approval.
- Configuration drift: The owner restores the trusted state or creates an approved change.
- Unexplained modification: Security investigates the host, process, identity, and related activity.
- Confirmed compromise: Incident response preserves evidence, contains the affected path, restores a trusted version, and reviews the baseline process.
The same discipline supports audit readiness. A FIM record is stronger when it shows the monitored scope, baseline ownership, event context, investigation, decision, and remediation. For SaaS organizations aligning security evidence with broader assurance work, SOC 2 solutions for SaaS compliance offer useful context, but a compliance framework shouldn't determine the entire detection strategy.
Operational principle: The objective isn't to accept fewer alerts. It's to make each high-value alert explainable, attributable, and actionable.
FIM won't replace SIEM correlation, endpoint detection, identity governance, secure deployment automation, or platform patching. It adds a precise integrity signal that those controls can interpret. The program stays effective when teams tune scope continuously, test response paths, protect their evidence, and revisit ownership whenever a DXP moves from server-based delivery to headless, composable, or managed services.
Kogifi designs, modernizes, and supports secure Sitecore, AEM, and Microsoft 365/SharePoint platforms, including headless XM Cloud architectures, CI/CD delivery, monitoring, incident response, and platform audits. Visit Kogifi to discuss how your team can connect file integrity monitoring with deployment governance, cloud operations, and practical response workflows.